Case Studies

Explore case studies of how our partners apply our insights to improve their processes, and get inspired by success stories of cybersecurity leaders dedicated to strengthening their resilience.
A finger pointing at a glowing node in a network of connected human figures, representing collaborative cybersecurity partnerships.
In 2011, the Agency for the Technological Modernization of Galicia (AMTEGA) was created to drive digitalization in the Spanish region. In 2020, AMTEGA partnered with Telefónica to raise awareness of cybersecurity and data protection among the citizens of Galicia and assist local government bodies in preventing cyberthreats and ensuring regulatory compliance. The main achievements of the PPP include:Developing and launching Galicia’s cybersecurity web portal, offering educational and informative content. Collaborating with regional TV to produce short cybersecurity videos, one of which introduced a cybercriminal character whose name became Galicia’s 2023 Word of the Year.Organizing more than 600 live lectures, reaching 15,000plus people, including specialized sessions for seniors. Building a strong social media presence, attracting 250,000-plus followers and accumulating 4.3 million-plus views.Hosting an annual Girls’ Talent in Cybersecurity event to encourage young women to explore careers in cybersecurity.Providing resources and advanced tools such as security information and event management (SIEM), automated penetration testing, vulnerability analysis, digital surveillance and consultancy services for data protection and information security.The partnership optimizes public-fund investments by delivering tangible projects. Services are implemented swiftly, using specialized personnel and the support of a technology company to develop solutions tailored to the needs of the Galician population and local institutions.
Spain
Telefónica and the Agency for the Technological Modernization of Galicia
Telefónica
In April 2023, Smart Africa, in collaboration with the Ministry of Communication and Digital Economy of Côte d’Ivoire, inaugurated an Innovation Centre in Abidjan. The centre is supported by École Supérieure Africaine des Technologies de l’Information et de la Communication and Hitachi Systems Security. The objective of the Innovation Centre is to build capacity in the cybersecurity sector across Africa. More specifically, it aims to provide training on cybersecurity skills to teachers.Each stakeholder involved in the partnership has a clearly defined role and responsibility. To illustrate, the private sector is responsible for resource mobilization and the provision of equipment to the centre, the ministry ensures oversight of the initiative and Smart Africa provides training content.
Côte d'Ivoire | IT and Communications (ICT)
Smart Africa Innovation Centre
Smart Africa Secretariat
The Trellix Emerging Students Cybersecurity Academy (TESCA) is a PPP focused on cultivating the next generation of cybersecurity professionals. Through its programme, Trellix collaborates with universities, with the primary objective of augmenting and expanding learning opportunities for students pursuing STEM education and, specifically, cyber-focused degrees or certificates. Trellix contributes its expertise through hands-on workshops and training sessions, covering real-world scenarios such as incident response, blue/red-team exercises and malware analysis. University partners facilitate student participation and provide academic context. The programme has engaged more than 200 students to date, equipping them with practical cybersecurity skills and knowledge. TESCA aims to broaden its outreach to additional universities throughout 2025, further amplifying its impact on cybersecurity talent development. As Trellix connects with students in TESCA it builds relationships and a pipeline for its early-career talent programmes, including internship and apprenticeship programmes that offer hands-on, real-world experience for students while they work on their programme degrees.
USA | IT and Communications (ICT)
Trellix Emerging Students Cybersecurity Academy (TESCA)
Trellix
The Western Balkans Cyber Capacity Centre (WB3C) and the University of Technology of Troyes (UTT) have partnered on a digital forensics programme to tackle the cyber skills gap. The 11-week programme, adapted from UTT’s N-Tech course, provides hands-on training to police investigators on cybercrime. WB3C, funded by France, Slovenia and Montenegro, offers trainers and facilities and covers travel and accommodation costs, while UTT supplies the curriculum and instructors. Each participant receives a laptop with installed specialized forensic software and, upon passing a final exam, a recognized qualification.This programme directly addresses the immediate shortage of skilled cybercrime investigators and digital forensics experts by upskilling professionals already in the field, reducing case backlogs and enhancing law enforcement capacity. As the progress of Western Balkans states towards EU accession primarily relies on judicial reforms, the need to enhance the institutional and operational capacities of law enforcement and achieve full interoperability is a priority. To ensure long-term impact, WB3C and UTT are working to embed the digital forensics curriculum into local university programmes. University faculty members have been invited to participate in the current course to familiarize themselves with the content and methodology, enabling them to deliver the programme to future generations of students. This approach, resembling the train-the-trainer model, aims to institutionalize digital forensics education and create a lasting pipeline of qualified cyber professionals. The programme also engages accreditation bodies, police academies and other essential stakeholders to develop a standardized and sustainable educational framework. The WB3C-UTT partnership exemplifies how public and academic sectors can collaborate to address both immediate skills shortages and long-term capacity building.
Montenegro, Serbia, Bosnia and Herzegovina, Republic of North Macedonia, Albania, Kosovo | Government, IT and Communications (ICT)
WB3C-UTT Partnership on Digital Forensics
Western Balkans Cyber Capacity Centre (WB3C)
Her CyberTracks is a global initiative designed to bridge the gender gap in cybersecurity by equipping women with essential skills and opportunities to succeed in the field. Her CyberTracks offers a comprehensive five-month curriculum that includes technical and soft-skills training, mentorship and inspirational networking events. In 2023 and 2024, Her CyberTracks trained 300 participants, achieving a 93% satisfaction rate and creating a vibrant network of cybersecurity professionals across Europe and Africa. By enhancing participants’ expertise and confidence, the initiative strengthens global cyber resilience and creates an inclusive cybersecurity workforce. The programme is based on strong partnerships: while funded primarily by the German Federal Foreign Office and supported by Microsoft, the initiative is co-implemented by the Deutsche Gesellschaft für Internationale Zusammenarbeit (GIZ), the International Telecommunication Union (ITU) and the United Nations Office on Drugs and Crime (UNODC). Local collaboration is also integral, with the Latin America and Caribbean Cyber Competence Centre (LAC4) supporting regional implementation, and public- and private-sector partners contributing in kind to the curriculum. This partnership model uses the strengths of each entity: international organizations provide strategic guidance and lead the implementation; private-sector partners offer industry expertise; and financial contributors ensure programme scalability.
Africa, Latin America | IT and Communications (ICT)
Her CyberTracks
Microsoft, German Agency for International Cooperation (GIZ), International Telecommunication Union (ITU)
The Inter-American Development Bank (IDB) is supporting, through financing, the promotion of cybersecurity and youth employment in Panama. The objective of this PPP is to develop skills and create jobs related to cybersecurity, focusing on improving women’s participation in the sector and expanding access to affordable cybersecurity services for SMEs. The entities involved in this alliance include NUMU Corporation, Deloitte Cyber Academy, Technical Superior Specialized Institute (ITSE), MNEMO Cybersecurity and various other organizations. NUMU Corporation is responsible for project management, skills development, bridges to employment and funds administration, while MNEMO Cybersecurity provides technical services and market experience. Deloitte Cyber Academy offers an online learning platform, while ITSE and other organizations assist in the outreach to young participants and host important activities related to the project. The impact of this alliance includes the establishment of a cybersecurity centre of excellence, the training and certification of 406 youngsters, 40% of them women, work experience for 200 of these individuals and the provision of cybersecurity services to 300 SMEs, enhancing their resilience to cyberattacks. NUMU is expanding this concept to El Salvador and other countries to open the highway of digital transformation opportunities for more people in the region. The goal is to make an impact through cybersecurity labs and AI skills development roadmaps, targeting the more vulnerable population in that country.
Panama | IT and Communications (ICT)
IDB: Promoting Cybersecurity and Youth Employment in Panama
Inter-American Development Bank
PPPs in cybersecurity offer a unique opportunity to enhance workforce development and drive economic growth. Cisco’s Networking Academy exemplifies this by equipping individuals with critical digital skills. Active since 1998 on the African continent, it trained more than 260,000 students in cybersecurity in 2024 alone in collaboration with schools, technical colleges, polytechnics and universities. And it doesn’t stop there. In addition, in collaboration with the South African government, the Edge Centre initiative supports small, medium and micro enterprises (SMMEs), which are crucial for innovation and job creation. This programme in South Africa is a strategic initiative under Cisco’s Country Digital Acceleration (CDA) programme, designed to drive digital transformation, innovation and skills development. This initiative addresses unemployment and skill shortages, aligning with national Memorandum of Understanding and the Broad-Based Black Economic Empowerment laws to promote economic inclusion and transformation. Edge Centres provide SMMEs with advanced Cisco technology and training, connecting them with global Cisco experts. This partnership transforms SMMEs into specialized technology partners and links Networking Academy graduates with employment opportunities, meeting business talent needs. This partnership highlights the transformative potential of PPP in cybersecurity, promoting innovation, economic growth and developing a future-ready workforce.
South Africa | IT and Communications (ICT)
Cisco Academy and Edge Centres in South Africa
Cisco
Morocco is working towards a new era of progress and modernization aimed at enhancing the quality and efficiency of the Higher Education, Scientific Research and Innovation (ESRI) environment. The nation is relying on younger generations to serve as a catalyst for advancing its developmental progress.The National Plan for Accelerating the Transformation of the ESRI Ecosystem (PACTE ESRI 2030) was launched by the Ministry of Higher Education, Scientific Research and Professional Training. The plan involves three main strategies: digital transformation, regulatory framework adaptation and national and international partnership opportunities.Fortinet joined the initiative in 2023 and has been working with the ministry under Code 212: An Innovative Network for Training the Digital Talent of Tomorrow. Code 212 aims to develop young people’s technological skills, encourage innovation and facilitate the country’s digital transformation. It also seeks to strengthen the tech environment and enhance youth employability. It offers training in four vital areas: coding, data, cybersecurity and systems and IoT (internet of things).Fortinet provides cybersecurity training and certification, at no cost to this initiative, through its Academic Partner Program. Through this partnership, Fortinet is actively supporting Code 212 schools – which span 12 state universities – by offering free training, hands-on labs and certification opportunities to students. Additionally, Fortinet is committed to training more than 25 educators nationwide, ensuring they develop strong expertise in Fortinet technologies and acquire the necessary skills to effectively teach their students.
Morocco | IT and Communications (ICT)
Fortinet and the Ministry of Higher Education, Scientific Research and Professional Training of Morocco
Fortinet
As part of Banco Santander’s commitment to law enforcement collaboration and work towards creating a more secure digital environment, the organization contributes to Europol’s annual training event held in Spain for law enforcement officers from multiple nationalities. During this event, Santander delivers a full day of training covering a range of topics, from quantum cryptography to a workshop on how ATM attacks are carried out. Santander has also provided in-depth, technical, hands-on training sessions. These sessions are tailored to address specific skill-building and emerging threats, covering areas such as digital forensics and cyber intelligence. The objective of the sessions is to equip Europol personnel with the practical skills and knowledge necessary to effectively investigate and mitigate complex cyberthreats, which will strengthen Europol’s capacity to safeguard infrastructure from evolving cyber risks.
Spain | IT and Communications (ICT)
Banco Santander and Europol
Banco Santander, Europol
The NotPetya cyberattack in 2017 significantly affected Mærsk’s short-term operational capabilities and customer service. More importantly, it marked a turning point in the company’s transition to a risk-based approach for cybersecurity investments and enhancements. Before initiating this transition, top leadership, in collaboration with stakeholders across the organization, assessed the business criticality of its applications and their roles in key business operations. This assessment provided the foundation for prioritizing investment areas effectively. Consequently, Mærsk adopted a quantified risk reduction strategy, translating risk into a “dollars-lost” equivalent, which facilitated meaningful discussions with the board and chief financial officer (CFO), ultimately securing essential funding for its cyber transformation programme. This strategy also guided decisions on where to invest in developing, operationalizing and embedding cyber capabilities. By using Monte Carlo simulations and other risk-modelling techniques, Mærsk enabled data-driven, risk-based decision making. This methodology has also significantly improved due diligence and purchasing decisions. The steps taken since 2017 have resulted in better investment prioritization, reduced cyber risk exposure and enhanced resilience across Mærsk’s operations.
Supply Chain & Transportation
Informed decision-making: Establishing a risk-based approach
When PETRONAS embarked on its digital transformation journey in 2017, leadership made cyber resilience a top priority from the outset. Following PETRONAS’ shift towards a more strategic and extensive use of data, technological solutions and new ways of working – as well as its role as the operator of national critical infrastructure – the need to operate securely became a non-negotiable prerequisite. However, an initial assessment of the organization’s cybersecurity posture indicated that substantial improvements were needed to keep pace with its increasingly complex operations and digital initiatives.Driven by a clear leadership mandate, PETRONAS began building its cyber resilience capabilities in 2018, focusing on five major pillars:Enterprise cybersecurity governance: Establishing a holistic framework for managing and enabling cybersecurity consistently across the groupCyber defensive operations: Ensuring effective identification, detection and response to cyber threatsIdentity and access: Enhancing clarity and control over who has access to what and whenReal-time operational technology (OT): Enabling better visibility of and response to threats in the OT environmentExtensive enterprise-wide education and awareness programme: Supporting all pillars by ensuring employees understand their role in protecting both themselves and the organization against cyber threats.Ultimately, executive leadership ensured that cybersecurity was not just viewed as an IT concern but as a business imperative, providing the necessary support and advocacy for the intensive three-year programme while integrating it into corporate decision-making. As a result, PETRONAS elevated its security posture from reactive to proactive, establishing cyber resilience as an actionable agenda at every level of the organization.
Leading organizational change: A cyber resilience transformation
Trust is at the core of Schneider Electric’s business, with cybersecurity as a critical pillar. Effective cyber risk management extends beyond technology to governance, which is why the company has embedded key internal controls (KICs) within the three-lines-of-defence framework. The KICs initiative establishes clear accountability for cyber risk mitigation, ensuring that business and operational cyber risk-owners (first line of defence) formally acknowledge risks and implement controls. These efforts are guided by the group CISO (second line of defence) and independently reviewed by internal audit (third line of defence). By making control expectations explicit, KICs eliminate ambiguity and ensure that cybersecurity and product security are integral to operations. KICs are mapped to company policies and the cyber risk register, which are updated annually by the cybersecurity team. Each year, risk-owners formally sign off on control execution, providing evidence or action plans to address gaps. This structured approach strengthens compliance, enhances business resilience and enables the company to demonstrate security commitments to customers and regulators. By formalizing risk-ownership, KICs mark a significant advance in Schneider Electric’s cyber maturity programme, reinforcing the company’s proactive stance on cybersecurity and business continuity.
Key internal controls in action
Critical information infrastructure (CII) is essential to the functioning of societies, supporting daily life and powering key sectors such as energy, healthcare, finance, telecommunications and transportation. As the systems become increasingly digital, ensuring their cybersecurity is vital to protecting public safety and economic stability. The Dubai Electronic Security Center (DESC), as the cybersecurity regulator in Dubai, plays a significant role in securing the emirate’s CII through a structured, risk-based approach reinforced by regulatory frameworks. In collaboration with the designated sector leads, DESC conducted rigorous risk assessments, mapping interdependencies that connect the various sectors to prevent cascading failures that could negatively affect the city’s economy and the well-being of its citizens. The Dubai Cyber Resilience Plan includes cybersecurity guidelines and measures for sector leads to implement, such as asset classification, disaster recovery, business continuity planning and incident response plans. To build the Dubai Cyber Resilience Plan, DESC identified critical sectors, ensuring the protection of critical services and assets that are the backbone of the city’s operations. The approach to fortifying Dubai’s digital infrastructure integrates regulatory oversight and strategic  cybersecurity initiatives, positioning the city as a global leader in cyber resilience.
Securing critical information infrastructure: Dubai’s cyber resilience approach
Cyber resilience cannot be achieved by the cybersecurity team alone; it requires the active engagement of key stakeholders throughout the organization. At Engro, regular tabletop exercises involve those critical stakeholders from information and communications technology (ICT), security, senior management, legal, public relations (PR) and operations to prepare for a serious cyber incident and evaluate the organization’s readiness to respond. These exercises follow a structured format that includes developing scenarios based on real-world threats, participant briefings, live role-playing of incidents and post-exercise assessments. A key focus is leadership engagement, with executives actively involved in decision-making simulations, crisis communication drills and impact assessments to replicate real-world cyber incidents.Past exercises have helped Engro to reveal gaps in detection, response, back-up validation, escalation procedures, decision-making and cybersecurity awareness across teams. Following the exercises, Engro implemented key improvements such as:Enhancing incident response plans with clearly defined roles and responsibilitiesStrengthening back-up and recovery strategies to ensure business continuityConducting targeted cybersecurity awareness training for employees, including senior management, streamlining communication between ICT, leadership and PR teams for faster decision-makingDeploying advanced security solutions and automation tools for real-time threat detection and responseThese measures have helped to enhance Engro’s cyber resilience, accelerate incident response times and strengthen crisis communication. Leadership involvement ensures that cyber resilience remains a top priority, emphasizing the need for proactive risk management and crisis preparedness.
Collaborating for cyber resilience: Engaging stakeholders across every level
As a leading global energy company, Repsol operates critical infrastructure in highly complex digital, cloud and industrial environments. With digitalization and innovation driving the company’s growth, ensuring protection against potential cyberthreats while preserving operational continuity presents a core priority of Repsol’s operations.Central to Repsol’s resilience strategy is continuous training and education for users, its business operations team and its technical team. This prepares the company to minimize the impact of cyberattacks by enhancing response speed and precision. Frequent crisis simulations with business continuity and technical tests are conducted to improve detection and response capabilities while strengthening the resilience of response teams under stress.Repsol integrates both red-team simulated cyberattack exercises and tabletop decision-making scenarios, sometimes with no prior notice. Employees from all locations participate, and some exercises escalate to the board level. Lessons learned from these exercises lead to continuous improvements, and to strategies and responses being refined.This comprehensive approach ensures Repsol’s cyber resilience is robust and adaptive, safeguarding its infrastructure and supporting ongoing digital growth by enabling quick and effective responses to cyber incidents.
Resilience in action: The power of training and simulations
UBS recognizes the industry-wide challenge of retaining operational resilience in the face of a dynamic cyberthreat environment and prioritizes the rapid recovery of critical business services following cyber incidents, including third-party outages. This reduces potential harm to clients, business operations and other market participants and minimizes downtime. The firm plans for severe scenarios, assuming critical services could be unavailable for an extended period. This assumption guides contingency planning, which focuses on:Workaround development: Collaborating with business units, the firm creates procedures to operate without impacted elements, prioritizing key processes to minimize impact.Data storage and access: UBS utilizes air-gapped vaulting solutions for storing critical applications and data in an immutable format, ensuring heightened security and expedited retrieval to recover key processes in the event of a cyberattack.Communication and coordination: The company has mature crisis management protocols providing clear communication channels between leadership, IT, business units and clients, ensuring fast and effective decision-making during an incident.Third-party risks: UBS assumes third-party services might take longer to recover or reconnection may be prolonged, and therefore focuses on developing effective and sustainable workarounds to mitigate those risks.By focusing on workarounds and strengthening resilience, UBS can continue operations with minimal impact following a cyber incident but also enhances overall agility, improves crisis response efficiency and builds greater confidence among clients and stakeholders.
Building cyber resilient business processes
Account compromise provides cybercriminals with a straightforward method of generating profit. By bypassing traditional security measures such as passwords and multifactor authentication (MFA), hackers can steal sensitive information, including personal details, financial data and log-in credentials. To address this concern, IMD Business School enforces strong password hygiene, number matching and context-based MFA prompts. It also strengthens phishing protection through security awareness training, advanced email filtering and risk-based access controls that block suspicious log-ins.However, acknowledging that not all compromises can be prevented, IMD Business School has established key damage control measures:Limit email exposure: Restrict the number of emails an employee can send within a set time frame to reduce phishing risks.Block self-service MFA registration: To prevent attackers from adding their own devices during an account compromise, users must contact IT Support to register new MFA devices.Restrict uploads of “IMD Confidential” files: Documents labelled “IMD Confidential” cannot be uploaded to unsanctioned cloud storage or external USB devices. Automatic labelling identifies sensitive files based on patterns such as files including 20+ email addresses.Block downloads to personal devices (“bring your own device” – BYOD): Prevents sensitive documents from being saved on unmanaged devices, reducing insider threats and data leaks.Through its proactive security practices, IMD Business School effectively reduces the number of successful account compromises. Equally important, IMD Business School’s robust damage control measures – restriction of certain functions – ensure that even if an incident does occur, the impact is minimized, safeguarding the organization’s sensitive data and systems.
A step ahead: Reducing account compromises and minimizing their impact
Building a security operations centre (SOC) is a complex endeavour that requires the balancing of speed, efficiency and quality in threat detection and response. Building a SOC comes with challenges such as ensuring an outcome-driven approach rather than a tool-centric one, maintaining scalability and standardization across operations, managing resource limitations and integrating emerging technologies while ensuring interoperability and effectiveness.Splunk’s approach to SOC operations addresses these challenges by focusing on quality and operational outcomes rather than simply resolving tickets quickly or deploying the latest security tools. This encompasses:Data-driven decision-making: Splunk ensures technology investments align with security outcomes, enhancing detection, response and resilience.Automation for efficiency: Automated processes reduce human error, ensure consistent responses and allow analysts to focus on higher-level tasks.Improved detection and response: Splunk achieves detection times of less than seven minutes for critical threats while enhancing collaboration and expanding services without adding resources.Partnership-driven innovation: Collaborating with vendors, including non-Splunk solutions, ensures tools meet operational needs and contribute to a stronger security ecosystem.Building an effective SOC requires more than just assembling security tools – it demands a strategic approach focused on outcomes, automation and continuous improvement. Splunk’s operations centre exemplifies this by ensuring high-quality, scalable security operations while promoting innovation through partnerships, ultimately strengthening overall resilience by enhancing adaptability and operational consistency.
Beyond “tooling”: A focus on quality and ecosystem collaboration
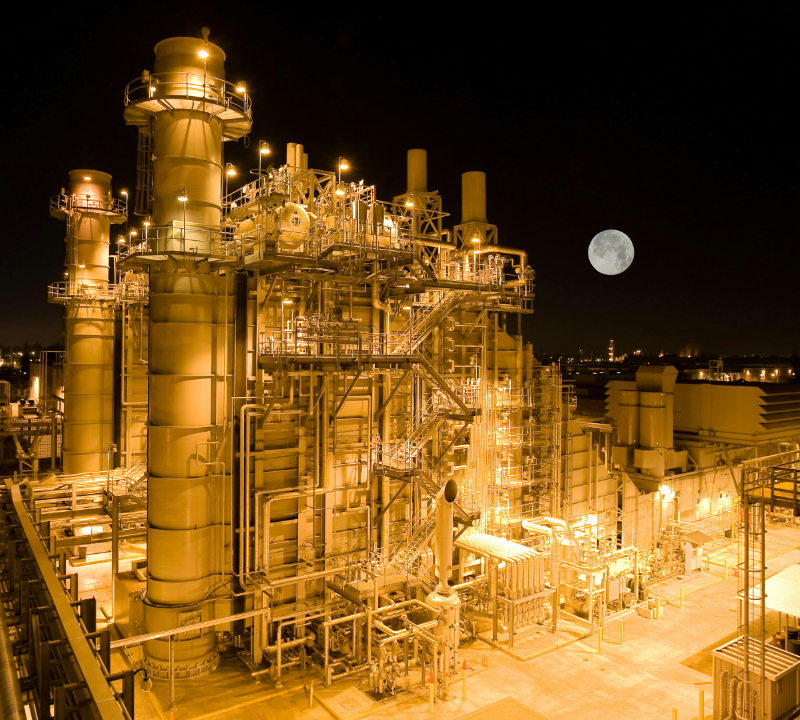
After acquiring the High Desert Power Plant in California, the private equity firm Middle River Power identified cyber threats to its operational technology (OT) assets as a critical risk. Limited visibility, evolving cyber threats and compliance challenges made it difficult to detect and respond to incidents effectively. To improve detection and response capabilities without disrupting operations, the company sought a comprehensive monitoring solution.Middle River Power collaborated with Siemens Energy to deploy managed detection and response (MDR) services at the plant. Siemens Energy’s analysts, operating from a remote security operations centre (SOC), leverage machine learning and OT expertise to continuously monitor and analyse data, enabling rapid detection of potential anomalies.Moreover, MDR helps Middle River Power to accurately determine which systems have been compromised in the event of an incident. The implementation of MDR also supports regulatory compliance by providing structured security reporting and audit-ready documentation.One immediate benefit of MDR was the early detection of an operational issue – an on-site historian that periodically overheated and rebooted. The system flagged this anomaly, enabling plant operators to resolve the issue before it escalated. Beyond identifying vulnerabilities, MDR allowed Middle River Power to accelerate incident response, reduce downtime and improve compliance efficiency, ultimately increasing the plant’s cyber resilience.
Accelerating detection and response: Strengthening OT resilience
Traditional IT service continuity plans – which are built around the assumption of physical threats such as natural disasters – often fail to adequately address the unique nature of modern cyberattacks, especially ransomware. Ransomware attacks do not just disrupt infrastructure in the same way as physical events; instead, they target primary and failover systems alike.Recognizing the growing threat of ransomware and the need for strong cyber resiliency, Henkel, a leading global company in adhesive technologies and consumer goods, took a proactive approach. To ensure rapid recovery and minimize downtime, the company undertook a comprehensive review of its IT architecture and continuity strategies, identifying several key initiatives:Green network for rapid recovery: An isolated “green network” across global sites and cloud infrastructure enabling the immediate recovery of operations independent of ongoing forensic investigations, ensuring the swift restoration of critical services.Prioritized recovery with immutable back-ups: Clear recovery priorities for business-critical workloads, alongside a robust back-up strategy that uses immutable back-ups to protect against data tampering.Enhanced end-user device recovery: Site-specific procedures for the rapid reimaging of end-user devices at scale (restoring or reinstalling an operating system and software to a known, secure state), reducing recovery times and minimizing disruptions.By addressing the specific challenges posed by ransomware, Henkel is significantly strengthening its cyber resilience. The new approach has enabled faster recovery, empowering the company to better withstand cyberthreats.
Rethinking IT resilience: Building recovery from ransomware