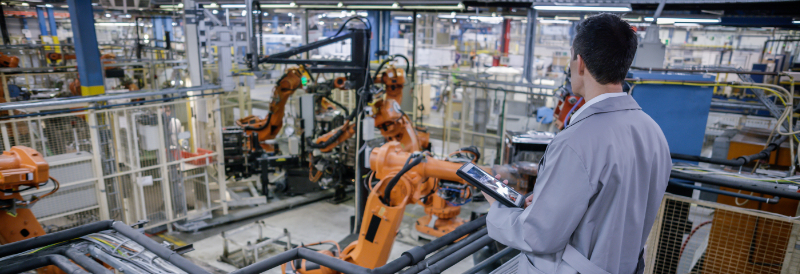
Schneider Electric’s cybersecurity strategy is multifaceted, covering the cybersecurity posture from IT to OT and from product design through installed base security. This strategy includes robust training and education of all its employees, both connected to and on the shop floor. This companywide, end-to-end, risk-informed approach has significant preventative measures (breach readiness) while being able to respond and recover in case of an incident (breach resilience). Schneider Electric achieves these programmatic objectives with:
- Employee training and awareness: The company aims to raise employee cybersecurity awareness, provide relevant training and create a culture to empower employees across both IT and OT to act in a secure manner. The training includes an annual baseline awareness course for all employees and role-based trainings for specialized populations including shop-floor personnel. All training is created with people at the centre and used to support a culture of shared ownership of the cybersecurity posture by all employees.
- An enterprise risk management (ERM) framework: Using a company-wide cyber risk register to categorize risk, the company translates cybersecurity risks into business and operational scenarios and exposure. This exposure is communicated with the C-suite to drive investments in risk-mitigation initiatives. This framework is aligned with the National Institute of Standards and Technology (NIST) Cybersecurity Framework and increases the company’s overall level of cyber resilience.
- Secure development lifecycle (SDL) management: The SDL journey began over 10 years ago and its mature programme encompasses defined and implemented security requirements, product testing, vulnerability management capabilities and a formal cybersecurity review before release(s). The company’s SDL programme is aligned to IEC 62443-4-1 and externally certified.
- Incident response capabilities: Schneider Electric is constantly testing and improving its capacity to respond to operational disruption, damage to customers, compliance issues and theft of intellectual property. Its incident response plans are defined and stress-tested routinely to ensure preparedness. A “Security Operations Center” operates 24x7x365 and is staffed with security analysts leveraging security incident and event management (SIEM) capabilities with OT scenario-based playbooks and responders.
The combination of these programmes ensures that cybersecurity risk is not an afterthought but part of the manufacturing management system.
Year published
21 May 2024 
Schneider Electric